Much more than granular control for your APIs in Kubernetes

mansplainer
João Brito
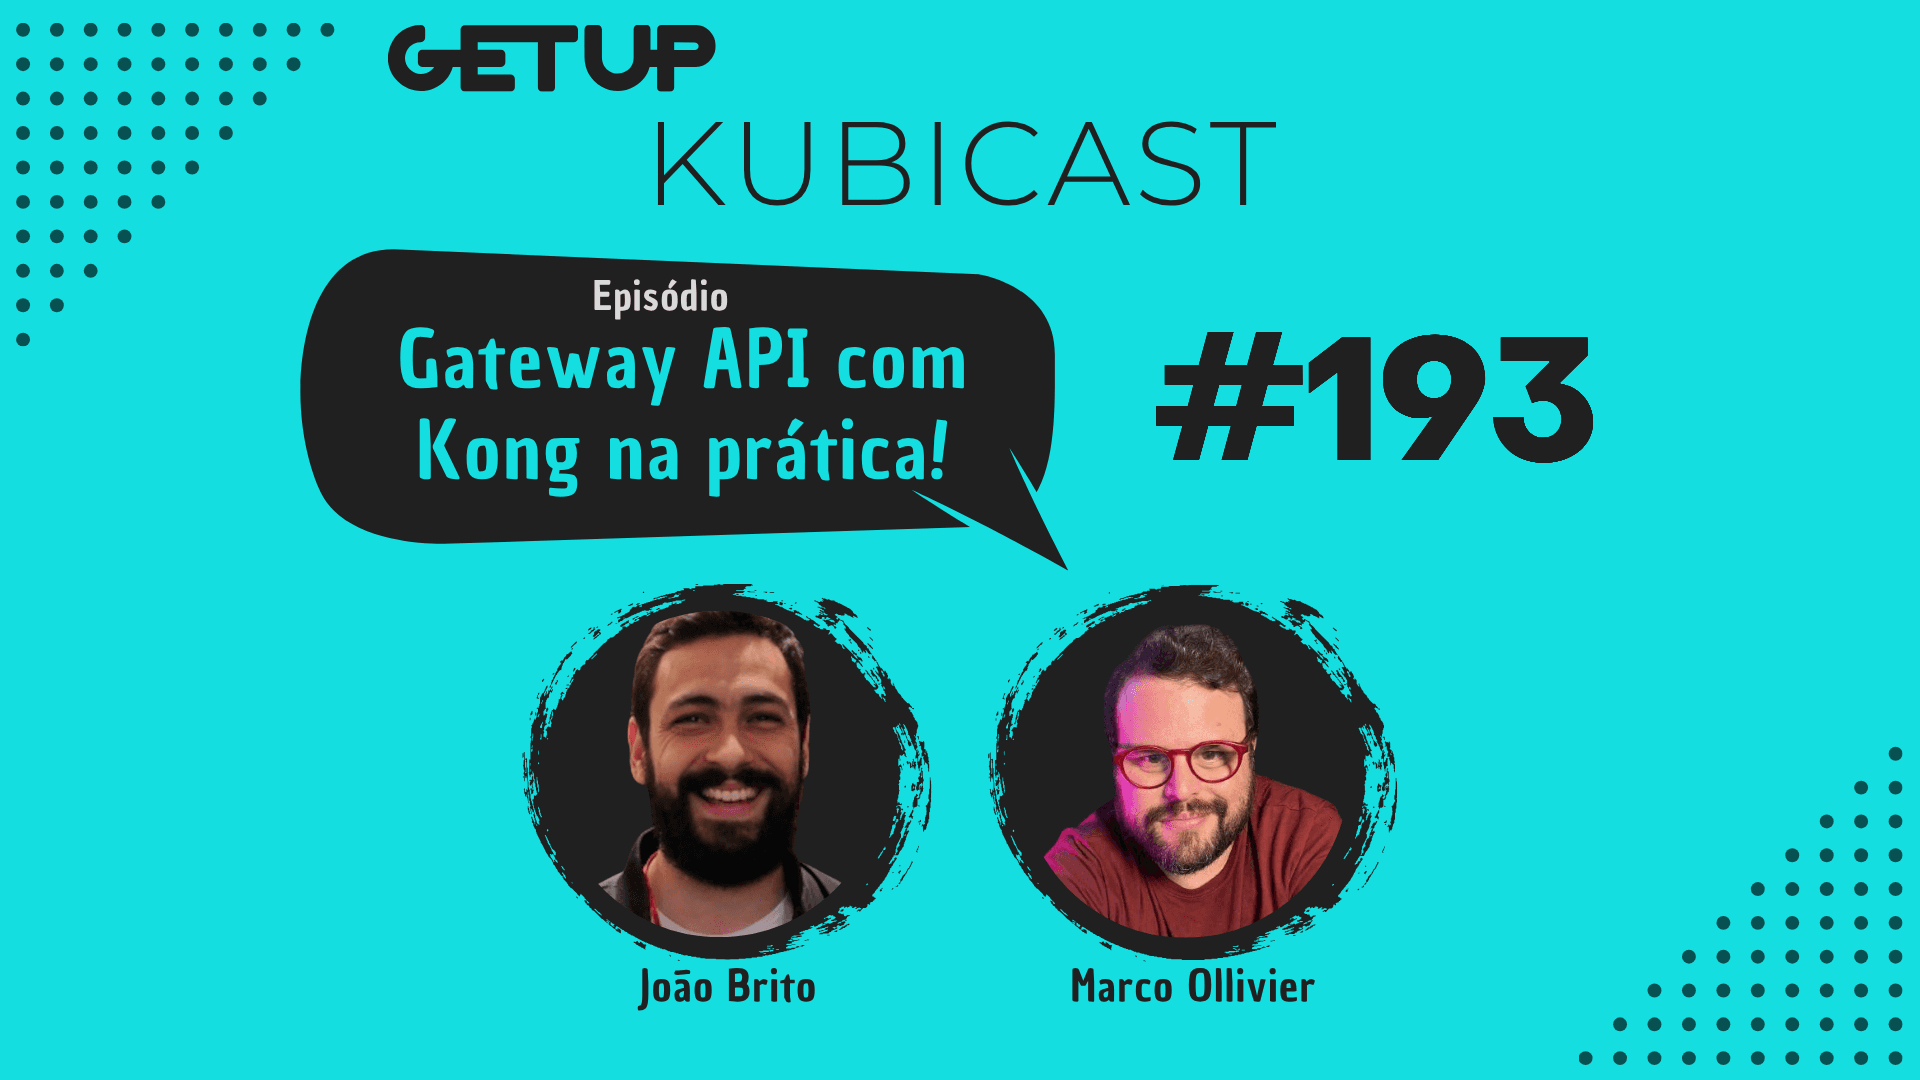
In this episode, we break down the path of HTTP traffic in Kubernetes — from reverse proxy to API Gateway — and discuss why Kong has become a key piece in cloud-native architectures. It's a talk about engineering, product decisions, and governance, not a webinar with terminal screenshots.
Why are we still talking about API Gateway?
Because the ecosystem has changed. Many people still use Ingress as a "Swiss Army knife", but the demands of versioning, security, granular routing, and governance have pushed the market towards more expressive models — and that's where standards like Gateway API come in. In the episode, we debate when a reverse proxy or a load balancer is enough and when the gateway becomes a necessity (think authentication, rate limiting, auditing, advanced routing, observability, and policies per team/product).
Where Kong fits into this story
The Kong was the common thread of the conversation: it's popular, flexible, and has a friendly adoption curve. The recurring highlight went to the ecosystem of "plugins" (yes, they appear a lot in the conversation): you can move authentication, tokens, simple business rules, and traffic limits to the edge — relieving services and standardizing practices. We talked about:
Extensibility: creation and customization of plugins (many teams start with ready-made ones and evolve to bespoke logic).
Governance: centralizing policies reduces entropy between squads and facilitates auditing.
DevEx: the gateway as an experience layer for those who publish APIs, with catalogs, conventions, and decent observability.
Reverse proxy, Load Balancer, and API Gateway: the boundaries
Throughout the episode, we map out the practical differences:
Reverse proxy: basic routing and connection termination.
Load Balancer: traffic distribution, health, and availability.
API Gateway: policy, identity, security, rate limiting, contextual routing, and telemetry applied to APIs.
The overlap exists, but the architectural intent changes. When the subject becomes product (contracts, versions, SLAs, and keys), the gateway is the right piece.
Security and identity at the edge
Recurrences from the talk: moving tokenization and verifications to the gateway, standardizing certificates, and avoiding logic duplication in each microservice. The message is pragmatic: it reduces cognitive cost, prevents implementation drift, and improves the experience of those who integrate APIs.
Observability: logs first, charts later
We talked a lot about logs and metrics as the basis for any troubleshooting and capacity. Tools like Grafana emerge as the natural destination for data, but the emphasis is on building the observability funnel from the gateway — standardizing fields and correlation.
OSS vs Enterprise: when paying makes sense
There is no silver bullet. The OSS edition meets many needs; the Enterprise version may make sense for advanced features, support, and governance at scale. The recommended criterion is opportunity cost: labor, engineering time, and operational risk.
About the guest
Marco Ollivier brings the practical vision of someone who implements and operates this type of architecture. The talk mixes technique, field experience, and business decisions — exactly what we like on Kubicast.
💡 Liked it? Listen to Kubicast #193 – Gateway API with Kong in practice on your favorite player and share with the team.
Newsletter Getup.
Atualizações sobre Kubernetes e Software Supply Chain Security todos os meses.
Operating Kubernetes in production for more than 13 years. With Quor, this experience extends to software supply chain security as well.
GET UP
© Getup · 2026